

Copyright © 2026 Cloud Native Bergen. All rights reserved.
Powered by Konf
Member of technical staff
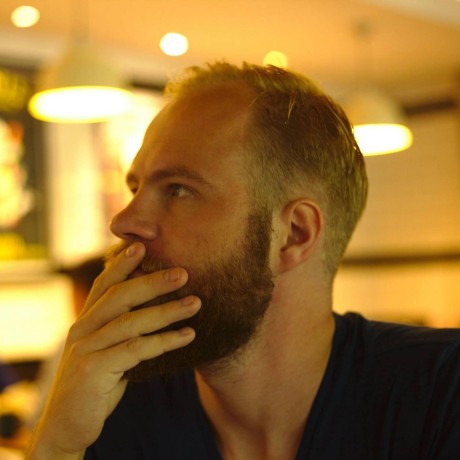
Kristoffer works as a dev at Tailscale, he is splitting his time between working on Tailscale and maintaining the open source project Headscale. Previously he worked as an SRE, building, monitoring and testing trading systems.
Infrastructure and services is increasingly getting spread across platforms and locations. One might run database and internal services on premise, while web services or customer facing services is running in Gigahost, Azure or AWS. Developers are run test jobs in GitHub Actions and want access to internal test data. Colleagues are out in the field with equipment truly on the edge of the network.
How do we even count the combination of things that need to talk together at any given time, securely, and effortlessly. Every platform and vendor pushes their own solution, you might have made your own, some web based, some VPN-based.
It rapidly gets complicated, everything needs to talk, but nothing talks together in the same way.
In this presentation, I will introduce you to Headscale and Tailscale. Headscale is an open source control server that lets you use Tailscale's powerful, yet simple "mesh" VPN client to solve all of these problems by giving you fixed IP-addresses for every device and service you need. It is your little private internet, when you need it.
We will set up a Headscale server live, and get started by building a network of machines, services, GitHub Actions, Kubernetes, SSH and end users.
In addition, we will look at how we can use powerful access controls to restrict access between users, services and parts of the network based on the users or services identity.
If you are setting up your laptop and a NAS, a Raspberry Pi, advance homelab, or use AWS, GCP, Azure and on premise at the same time, this could be the tool you have been missing.
Making safe connections, direct and effortless.